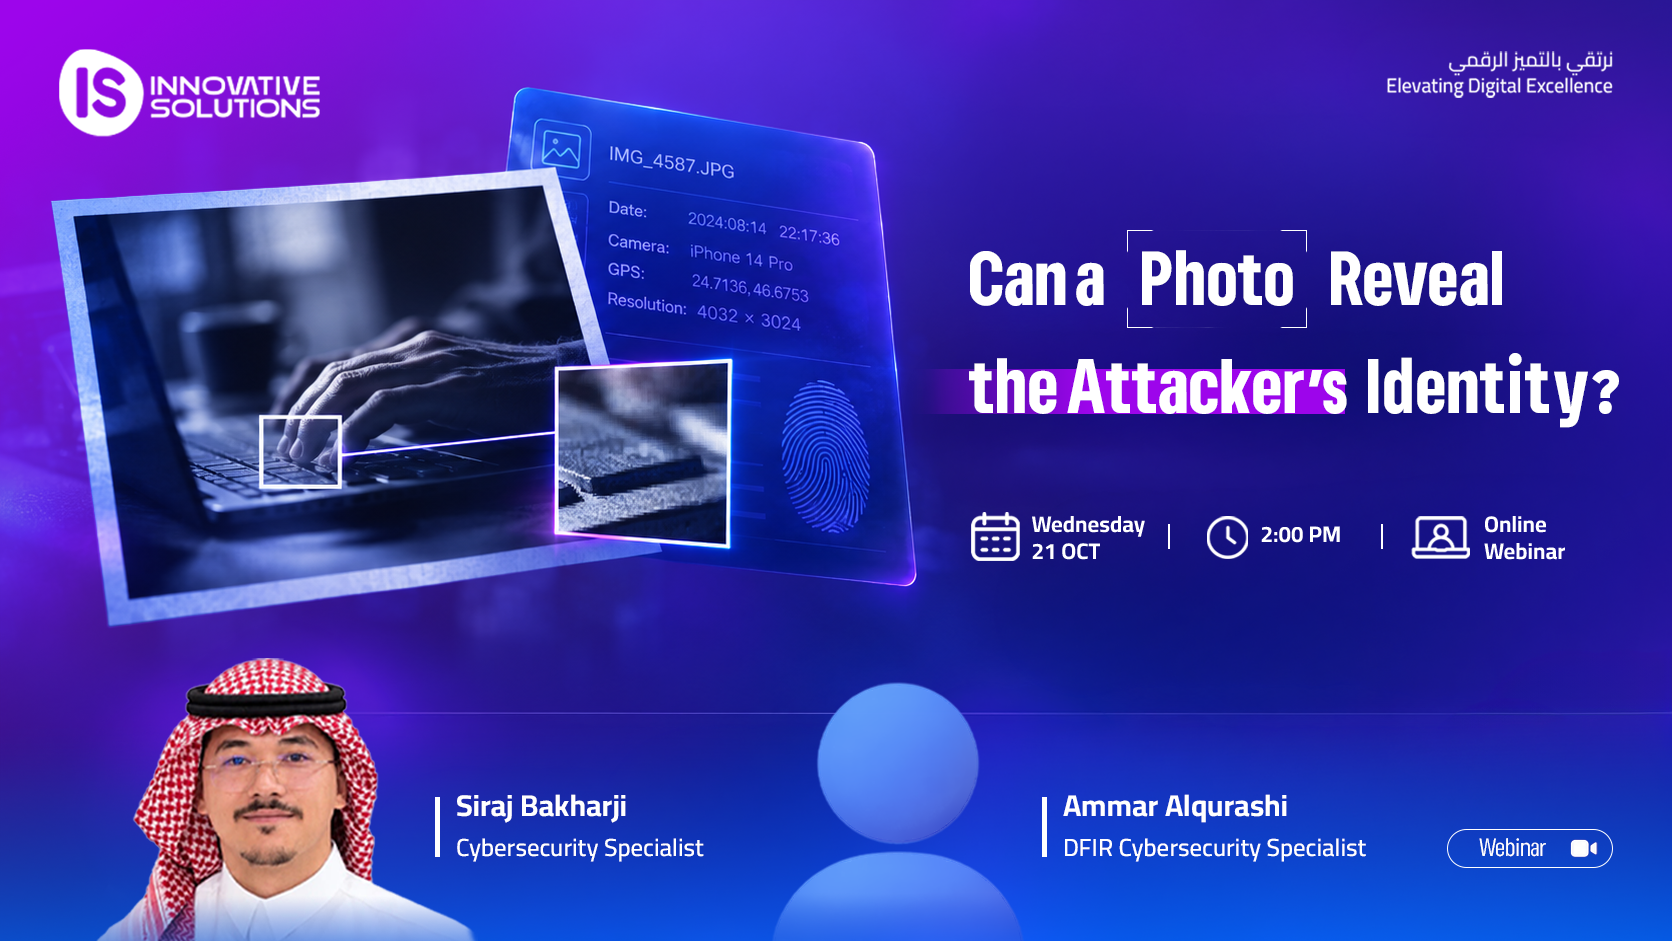
Can a Photo Reveal the Attacker’s Identity?
 Seraj Ghuni & Ammar Alqurashi
This webinar explores what a single photo can and cannot reveal in a security incident. Using a hypothetical case that begins with an image received from an unknown account, followed by a threatening message, it walks through how digital forensics is used to collect evidence, examine it, and link it to the incident, while making the distinction between finding a lead and proving an attacker's identity.
In this webinar, you'll learn:
- What digital forensics is and its five stages: collection, preservation, examination, analysis, and reporting
- Why the goal is not just finding information, but reaching conclusions that can be verified and defended with evidence
- The everyday situations that call for digital forensics, from fraud and extortion to data leaks, suspicious emails, unauthorized activity, and file origin checks
- How to preserve evidence before analysis: keeping the original untouched, documenting the context, working on a copy, calculating a SHA-256 hash, and recording every step
- What EXIF metadata can reveal about the device, capture time, location, and editing software, and the limits of relying on it
- A hands-on demonstration of extracting and reviewing a photo's metadata with ExifTool
- How investigators connect image data with the message, the account, the organization's records, and independent sources
- Why a single field inside a photo is not enough to identify an attacker, and how relying on it can lead to accusing the wrong person
- Why a photo with no EXIF data does not end the investigation
Whether you work in cybersecurity, handle incident response, or simply want to understand how digital evidence is evaluated, this webinar gives you a clear, practical view of how investigators turn a digital clue into a conclusion backed by evidence.
Register now to watch the full webinar!